Relying on Excel for Making Tax Digital (MTD) isn’t just risky; it’s a direct path to severe penalties and exposes your board to personal liability.
- Manual data handling inevitably breaks the mandatory « digital links » required by HMRC, invalidating your submissions from the outset.
- A standard cloud backup is not a legally defensible audit trail and offers zero protection against data tampering or regulatory scrutiny.
Recommendation: Implement a financial system built upon an immutable ledger to create a tamper-proof, legally sound, and continuously auditable record of all financial activity, effectively neutralising compliance risk.
For a Chief Risk Officer in the UK, the nightmare scenario is often deceptively simple: a single, flawed formula in a sprawling Excel sheet that goes unnoticed until a letter from HM Revenue & Customs arrives. The resulting audit isn’t just a financial drain; it’s a direct challenge to the firm’s governance and integrity. Many organisations believe they are mitigating this risk by using « HMRC-approved » bridging software or simply telling their teams to « be more careful. » This approach is fundamentally flawed and dangerously naive. It treats the symptoms—human error and process gaps—without addressing the root cause.
The core of the problem lies not in the occasional mistake, but in the very architecture of the systems used for financial reporting. While the common advice focuses on software features and user training, it misses the crucial point that has significant legal ramifications for company directors. The real conversation isn’t about avoiding a minor penalty; it’s about building a legally defensible compliance framework. But what if the key wasn’t just better software, but a completely different philosophy of data integrity? This article deconstructs the specific technical failures that lead to severe penalties and director-level liability, demonstrating how to build an automated compliance system that moves beyond simply ticking boxes to create a genuine, unshakeable fortress around your firm’s financial data.
This guide will dissect the structural weaknesses of common approaches and lay out a strategic framework for implementing a truly rigorous and automated risk management system. We will explore why traditional methods are doomed to fail and how a shift in technological strategy can protect your firm and its directors from the most severe consequences.
Summary: A Strategic Framework for Automated HMRC Compliance and Risk Mitigation
- Why Does Relying on Excel for Making Tax Digital Guarantee Severe HMRC Penalties?
- How to Build an Unbreakable Audit Trail Within Your Native Accounting Software?
- Cloud Backup vs Immutable Ledger: Which Secures Your Compliance Data Best?
- The Outdated Software Oversight That Exposes Your Board to Director-Level Legal Action
- Automating VAT Calculations Across Complex Cross-Border European Transactions
- The Customs Compliance Oversight That Delays Essential Deliveries by Weeks
- The Scenario Planning Oversight That Leaves Enterprises Vulnerable to Sudden Shocks
- How to Implement a Rigorous Risk Assessment Framework for Major Corporate Investments?
Why Does Relying on Excel for Making Tax Digital Guarantee Severe HMRC Penalties?
The reliance on Microsoft Excel for financial reporting is the single greatest point of failure in modern corporate compliance. While it’s a versatile tool, its fundamental architecture is incompatible with the core principle of HMRC’s Making Tax Digital (MTD) initiative: the unbroken digital link. MTD mandates that data must flow from the source transaction to the final VAT return submission without manual intervention. Copying and pasting data between spreadsheets, or manually re-keying figures into a bridging software template, explicitly breaks this digital link. This isn’t a minor procedural oversight; it invalidates the entire submission from a legal standpoint.
HMRC’s penalty structure may seem lenient at first glance, starting with a points-based system that can lead to a financial penalty. However, this masks the true scale of the risk. The systemic issue is poor record-keeping, which is an inherent feature of spreadsheet-based workflows. It is no surprise that an analysis of compliance cases found that poor record-keeping was a factor in 65% of cases that resulted in penalties, with fines far exceeding the initial figures. The moment an auditor discovers a broken digital link, they are empowered to question the integrity of all your financial data, triggering a far deeper and more costly investigation.
Using Excel with bridging software is not a sustainable strategy; it’s an active acceptance of systemic risk. The lack of version control, user access logs, and formula validation creates a black box of potential errors. You are not just risking a penalty; you are building your compliance framework on a foundation that HMRC has explicitly designed its regulations to reject. Persisting with this approach is a guarantee of eventual, and severe, regulatory action. The question is not *if* it will fail, but when, and how significant the fallout will be.
How to Build an Unbreakable Audit Trail Within Your Native Accounting Software?
An « unbreakable » audit trail is not merely a log of activities; it is a legally defensible, chronological record of every single financial event within your organisation. From a UK regulatory perspective, this means capturing not just the ‘what’ and ‘when’, but also the ‘who’ and ‘why’ for every transaction and data alteration. Native accounting software provides the foundation for this, but only if it’s configured to move beyond basic compliance and towards advanced protection. The standard for a robust audit trail requires complete financial transaction records with user identification, precise timestamps, and details of any data alterations. Crucially, these records must be retained for statutory periods, which can be up to eight years depending on the specific sector and regulations like GDPR, FCA, or HMRC rules.
The distinction between a basic log and a fortress-like audit trail is critical. A basic system might log a username and a timestamp, but an advanced system captures the user’s IP address, the ‘before’ and ‘after’ values of any changed data, and a mandatory field for the reason behind the change. This transforms the audit trail from a simple record into a powerful deterrent against both internal fraud and external scrutiny. It creates a system of accountability where every action is transparent and traceable. The goal is to create a data environment where unauthorised or illogical changes are not only difficult but leave behind an indelible digital footprint.
To understand the gap between minimum requirements and true security, consider the following comparison. A system that merely meets basic compliance is a wooden fence; a system built for advanced protection is a reinforced concrete wall.
| Feature | Basic Compliance | Advanced Protection |
|---|---|---|
| User Activity Logging | Username and timestamp only | IP address, pre/post values, reason for change |
| Document Attachment | Manual upload | Auto-link invoices to transactions |
| Error Detection | Basic validation | Automated anomaly alerts |
| Data Retention | Standard backups | Immutable audit logs with WORM storage |
This table highlights that true security isn’t about having a feature, but about the depth and automation of that feature. Automating the linking of invoices, detecting anomalies in real-time, and ensuring data cannot be altered are the hallmarks of a system designed to withstand a rigorous HMRC audit, not just to file a VAT return.
Cloud Backup vs Immutable Ledger: Which Secures Your Compliance Data Best?
A common and dangerous misconception in corporate governance is equating a cloud backup with a secure, compliant data record. A cloud backup is simply a copy of your data, stored elsewhere. It is, by design, mutable—it can be overwritten, corrupted, or even maliciously altered. If your primary data is flawed, your backup is merely a perfect copy of that flawed data. For regulatory purposes, particularly under the scrutiny of an HMRC audit, a standard backup offers almost no verifiable proof of data integrity over time. It cannot prove that a record has *not* been changed. This is a critical failure from a legal standpoint.
This is where the concept of an immutable ledger, often associated with blockchain technology, becomes a game-changer for compliance. An immutable ledger is a write-once, read-many database. Once a transaction is recorded, it cannot be altered or deleted without breaking the entire chain of subsequent records—an action that is immediately detectable. As leading compliance analysts note, true audit trail compliance requires a system that is inherently tamper-proof. As stated by experts on a leading compliance blog, UK requirements demand a system that is fundamentally tamper-proof. They point out that in the UK, audit trail compliance requires automated, tamperproof, and chronological logs of financial transactions. This isn’t a feature; it’s the core architectural principle.
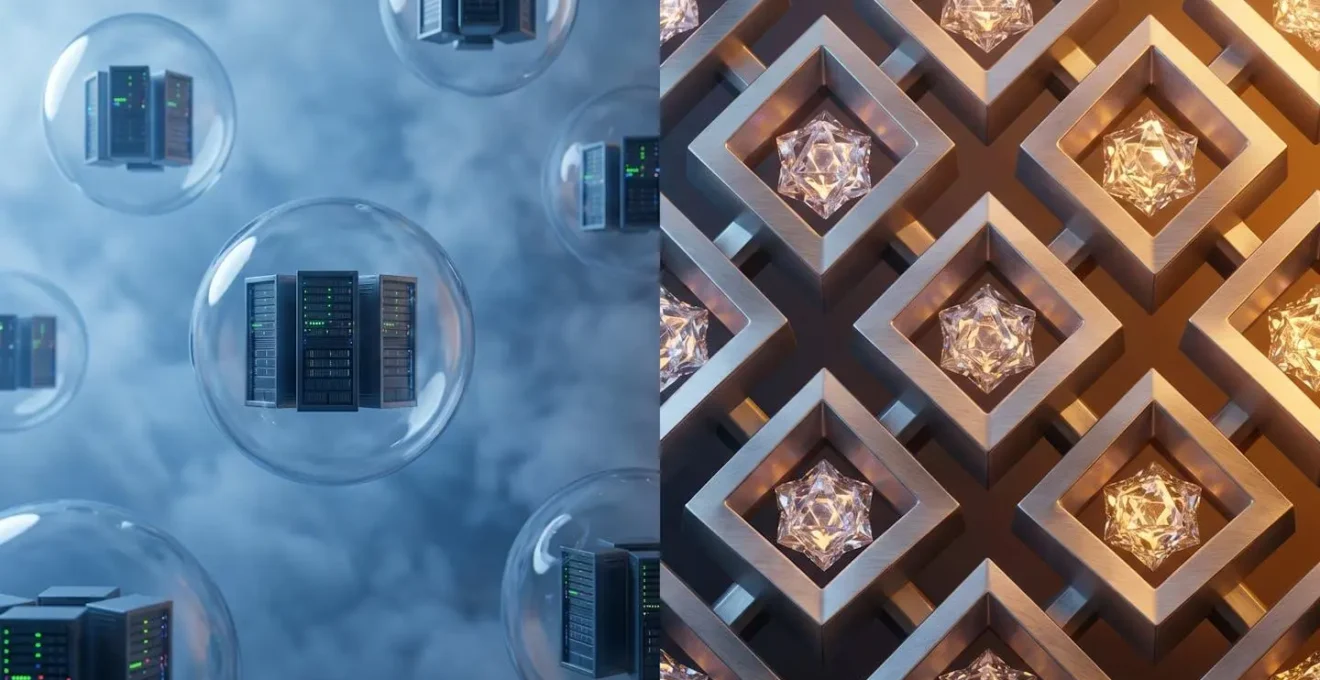
The visual distinction is stark: cloud storage is a series of separate, vulnerable data points, whereas an immutable ledger is an interlinked, unbreakable chain. This architectural difference provides the non-repudiation that a legal challenge or regulatory audit demands. You can prove, with mathematical certainty, that the record of a transaction from three years ago is exactly as it was when it was first recorded. A cloud backup can only show you what the data looked like at the moment of the last backup. For a CRO, the choice is clear: one is a convenience, the other is a legal defence.
The Outdated Software Oversight That Exposes Your Board to Director-Level Legal Action
The continued use of outdated or inappropriate financial software is no longer a simple operational inefficiency; it is a significant governance failure that carries personal risk for company directors. Under UK law, directors have a duty of care to ensure the company maintains adequate and accurate financial records. In the context of MTD, this duty extends to ensuring the systems and processes are compliant with specific digital record-keeping and submission requirements. Pleading ignorance of the technology or delegating responsibility to the finance team is not a valid defence. When a company is found to be systematically non-compliant due to a reliance on manual processes or broken digital links, HMRC can and will look beyond the company to the individuals responsible for its governance.
The issue is escalating. The MTD for Income Tax Self Assessment (ITSA) is on the horizon, with a massive expansion of the program. According to House of Commons Library research, HMRC estimates indicate that 864,000 taxpayers will be brought into the MTD for ITSA regime from April 2026. This demonstrates HMRC’s clear and unwavering commitment to digital-first compliance. For any board, ignoring this trend is a dereliction of duty. If the company’s core financial system is architecturally incapable of meeting these evolving standards, the board is knowingly presiding over a non-compliant organisation.
This creates a direct line of sight from a technical failure (e.g., using Excel) to director-level legal action. An investigation that reveals a persistent and wilful disregard for MTD’s core principles—such as maintaining digital links—can be construed as a failure of directorial duty. The consequences can range from substantial personal fines to, in the most extreme cases, disqualification as a director. The software you use is no longer just an IT decision; it is a declaration of your board’s commitment to good governance and the rule of law. A CRO’s primary role is to identify and mitigate such enterprise-level risks, and there is no greater risk than one that puts the board’s own liberty in jeopardy.
Automating VAT Calculations Across Complex Cross-Border European Transactions
The complexities of VAT in a post-Brexit world have created a minefield for UK businesses trading with the EU. What was once a relatively streamlined process is now a labyrinth of different VAT rates, rules of origin, and import/export declarations for each member state. Attempting to manage this complexity manually is not just inefficient; it’s a recipe for costly errors, shipment delays, and regulatory penalties. The sheer volume and variability of rules mean that a human-led process, even one supported by spreadsheets, is guaranteed to fail.
For instance, the VAT treatment of goods can depend on their classification, their ultimate destination, the status of the buyer, and the specific trade agreements in place. A single mistake in applying the wrong country’s VAT rate or failing to reclaim input tax correctly can have significant financial repercussions. Automation is the only viable path to navigating this landscape with any degree of accuracy. Modern compliance platforms use AI-driven systems to manage this. They can automatically classify transactions, apply the correct, up-to-the-minute VAT rates for any given EU country, and handle the complexities of cross-border compliance. This ensures that as regulations change, the system adapts instantly, preventing the miscalculations that lead to penalties.
This isn’t just about calculating the correct VAT. It’s about creating a seamless flow of data from the point of sale to the final customs declaration and VAT return. An automated system can generate the correct documentation for each shipment, communicate directly with customs systems, and reconcile payments against invoices and declarations. This level of integration turns a complex, multi-stage process into a single, automated, and fully-auditable workflow. For a CRO, this removes a huge area of operational and financial risk, transforming the EU trade corridor from a source of anxiety into a predictable and compliant part of the business.
The Customs Compliance Oversight That Delays Essential Deliveries by Weeks
Beyond VAT, the physical movement of goods across the UK-EU border presents another critical risk vector: customs compliance. An oversight as simple as an incorrect commodity code or missing proof-of-origin documentation can lead to goods being held at the port for days or even weeks. These delays are not just logistical headaches; they have immediate and severe financial consequences. They can halt production lines, lead to missed contractual deadlines, and damage client relationships. Furthermore, the financial sting is direct: incorrect declarations can lead to underpayment or overpayment of customs duties and import VAT. In the UK, UK import VAT is calculated at 20% on the full customs value plus any applicable duties. An error here can result in a significant, unexpected cash flow burden and potential penalties from HMRC.
Manual management of customs documentation is a high-risk activity. It relies on staff having perfect, up-to-date knowledge of the UK Global Tariff, free trade agreements, and the specific requirements of both UK and EU customs authorities. This is an unrealistic expectation. The only way to mitigate this risk effectively is through automation. By integrating supply chain and financial data directly with customs systems, firms can automate the generation and submission of transit documents, simultaneous export/import declarations, and commodity code classifications. This dramatically reduces the potential for human error and creates a clear, auditable trail for every shipment.
The strategic imperative is to remove human intervention from the repetitive and rule-based aspects of customs clearance. An automated system ensures consistency, accuracy, and speed, turning customs from a bottleneck into a smooth and predictable part of the supply chain. For a CRO, this is a clear win, reducing operational disruption and financial uncertainty.
Action Plan: Automating Customs Documentation
- Implement transit documents for EU-UK trade to reduce paperwork at the border.
- Set up fiscal representation for EU imports to manage VAT without needing a separate registration in each country.
- Configure systems for simultaneous, linked export and import declarations to streamline the process.
- Establish robust origin proof systems (e.g., Registered Exporter system – REX) to benefit from free trade agreements.
- Automate commodity code classification using AI-powered tools to ensure accuracy and consistency.
- Connect supply chain and ERP data directly to customs systems to eliminate manual data entry.
The Scenario Planning Oversight That Leaves Enterprises Vulnerable to Sudden Shocks
Effective risk management is not just about dealing with current regulations; it’s about anticipating future changes and building resilience. Many enterprises are dangerously myopic, focusing only on the immediate compliance deadline while ignoring the clear trajectory of regulatory change. The phased rollout of Making Tax Digital is a perfect example. While the focus has been on MTD for VAT, the roadmap for MTD for Income Tax Self Assessment (ITSA) is already defined and approaching rapidly. According to detailed guidance, MTD for Income Tax will apply to those with income above a £50,000 threshold from April 2026, with the threshold dropping to £30,000 from April 2027. Businesses that believe this doesn’t affect them are failing at basic scenario planning.
This oversight leaves them vulnerable to a sudden « compliance shock »—a point where their current systems and processes become catastrophically obsolete overnight. The transition to a new compliance regime is not trivial. It requires investment, training, and process re-engineering. By failing to plan for the inevitable expansion of MTD, firms are choosing to absorb these costs and disruptions under extreme time pressure, which is when mistakes are most likely to happen. A proactive approach involves evaluating and implementing systems that are not just compliant with today’s rules, but are architecturally flexible enough to adapt to tomorrow’s.
This requires a shift in mindset from reactive compliance to proactive risk modelling. A CRO should be asking: « What if the MTD threshold drops further? What if quarterly reporting is extended to Corporation Tax? Is our current software stack capable of handling these scenarios without a complete overhaul? » If the answer is no, then the organisation is carrying a significant, unacknowledged risk. A system designed for the future will handle these changes as simple configuration updates, while a system designed only for the present will fracture under the pressure of regulatory evolution.
Key Takeaways
- Relying on Excel and manual processes for MTD is not a calculated risk; it is a guaranteed compliance failure that breaks mandatory digital links.
- A legally defensible audit trail must be more than a simple log; it must be an immutable, tamper-proof, and chronological record of all financial activity.
- The choice of financial software is a board-level governance decision, and using outdated systems creates a direct path to personal, director-level liability.
How to Implement a Rigorous Risk Assessment Framework for Major Corporate Investments?
Implementing a rigorous risk assessment framework for a new compliance system is not a standard IT procurement exercise. It is a major corporate investment in governance and resilience. The primary failure of most assessment processes is that they focus on features and price rather than on architectural integrity and legal defensibility. A rigorous framework must begin with the principle that any system relying on manual workarounds or disconnected spreadsheets is an immediate disqualification. As the Institute of Certified Public Accountants UK (ICPA) warns, such systems break the digital link that HMRC requires, potentially invalidating all submissions and creating a huge workload during an audit.
The assessment must be led by risk and legal criteria first, and functional requirements second. The core questions should be: Does this system create an immutable audit trail? Can it prove, to a legal standard, that data has not been altered? Does it have the granular access controls to enforce segregation of duties? Does it integrate seamlessly with other systems to prevent manual data entry at any point in the process? These are not IT questions; they are governance questions.
Your due diligence checklist for a new compliance system should therefore look less like a feature comparison and more like a legal discovery document. It must verify the software’s official HMRC approval, but this is merely the entry ticket. The real assessment lies in testing its resilience. This involves verifying its support for all required submissions (quarterly and annual), its integration capabilities, its multi-user permission controls, and, critically, its disaster recovery and backup procedures. The total cost of ownership must be calculated not just in pounds, but in the reduction of risk exposure for the board. The right investment eliminates risk; the wrong one merely hides it until it’s too late.
The ultimate goal is to shift the organisation’s posture from reactive compliance to proactive, automated risk mitigation. This requires a system that is not only compliant by design but also transparent, auditable, and legally robust. To begin this process, the next logical step is to conduct a thorough audit of your current systems against the rigorous criteria of a legally defensible framework, identifying every broken digital link and manual intervention point.